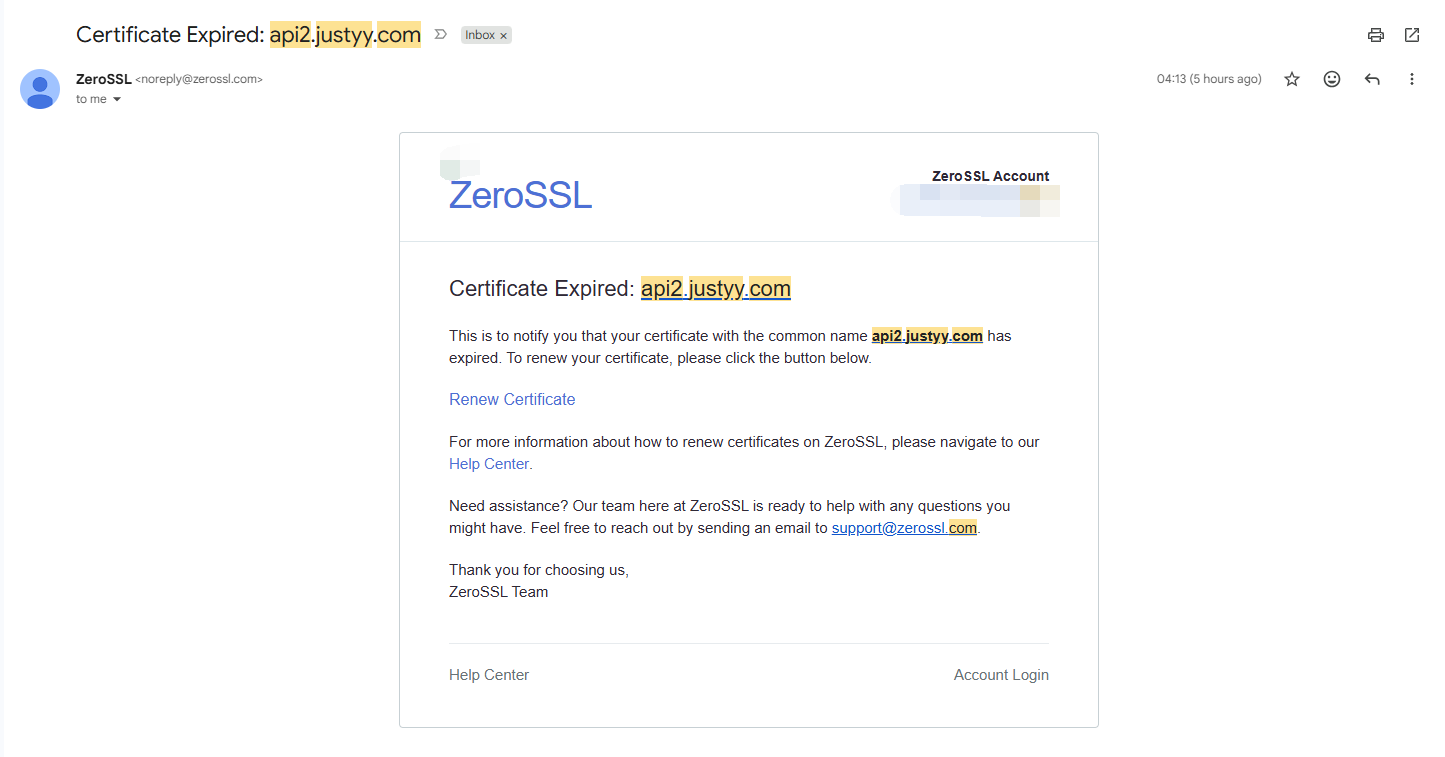
Renewed: Certificate Expired: api2.justyy.com
Renewed: Certificate Expired: api2.justyy.com
Steem to the Moon🚀!
- You can rent Steem Power via rentsp!
- You can swap the TRON:TRX/USDT/USDD to STEEM via tron2steem!
- You can swap the STEEM/SBD to SUI via steem2sui!
- You can swap the STEEM/SBD to SOL Solana via steem2sol!
- You can swap the STEEM/SBD to ETH Ethereum via steem2eth!
- You can swap the STEEM/SBD to Tether USDT (TRC-20) via steem2usdt!
- You can swap the STEEM/SBD to TRX (TRON) via steem2trx!
- You can swap the STEEM/SBD to BTS (BitShares) via steem2bts!
- Register a free STEEM account at SteemYY!
- Steem Block Explorer
- ChatGPT/Steem Integration: You can type !ask command to invoke ChatGPT
- Steem Witness Table and API
- Other Steem Tools
Support me, thank you!
Why you should vote me? My contributions
Please vote me as a witness or set me as a proxy via https://steemitwallet.com/~witnesses
Great work tracking the SSL renewal—did you run into any specific challenges with the Let’s Encrypt auto-renewal script? 🚀🔧✨
Good reminder on the SSL renewal cycle. One thing that often gets overlooked: keeping track of certificate expiry dates across multiple API endpoints gets complex fast, especially if you're managing several domains.
Raw WHOIS data shows you registrant info and basic domain records, but structured domain monitoring for certificates, nameserver changes, and expiry alerts is another layer. WhoisFreaks.com returns parsed WHOIS plus certificate tracking data so you catch renewals before they lapse, rather than discovering it through downtime like some teams do.
Automation catches the technical renewal, but monitoring the domain health itself prevents surprises downstream.